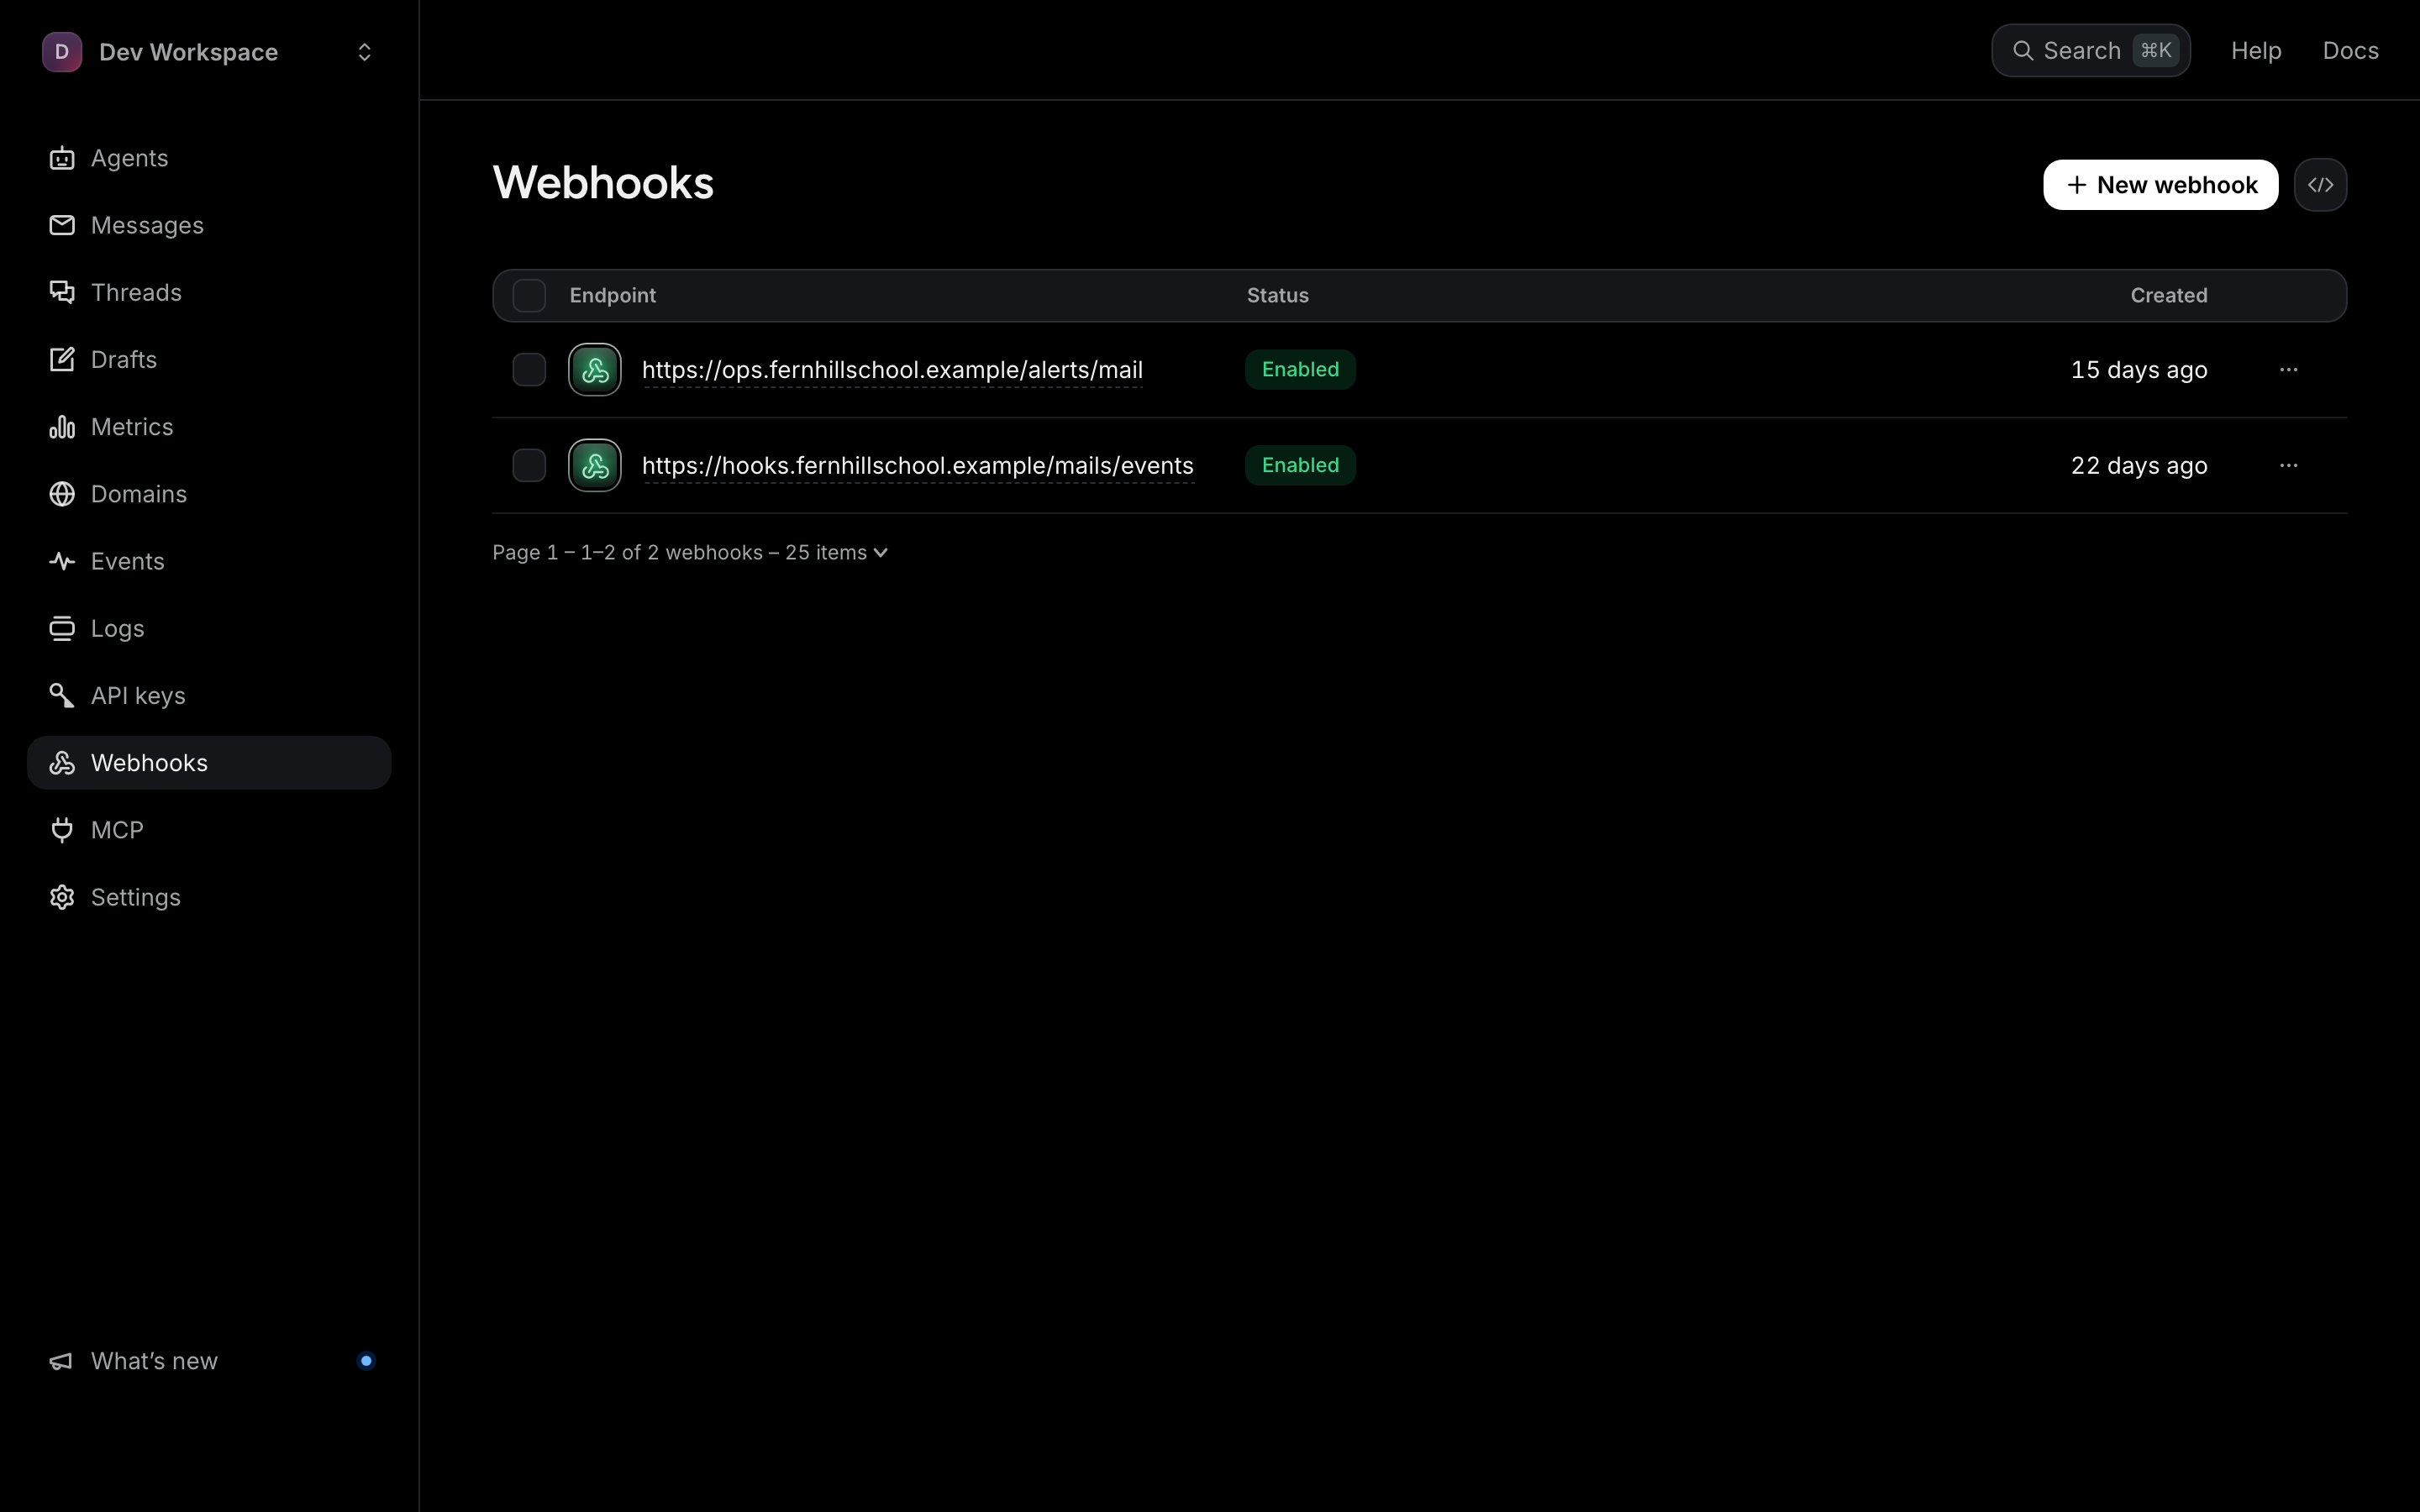
Add an HTTPS endpoint, choose the events you want, and every matching event is POSTed to you.
Verifying the signature
Each delivery carries X-Mails-Signature in the form t=<timestamp>,v1=<signature>: an HMAC-SHA256 of the timestamp, a dot and the raw request body, keyed with your endpoint's signing secret, with a ±5 minute timestamp tolerance. Both SDKs check it for you: webhooks.verify in TypeScript, verify_webhook in Python. Verify against the raw body, before any JSON parsing — a re-serialised body will not match, and that is the single most common integration bug here.
Retries
A non-2xx response, or no response within 5 seconds, is retried twice with backoff, so three attempts in all. After the third failure the delivery lands in the dead-letter queue, where it is kept and can be replayed once your endpoint is healthy again. Nothing is silently dropped.
Testing without waiting for real mail
Send test event on the Webhooks page, or POST /v1/webhooks/{id}/test, fires a signed webhook.test delivery at your endpoint, so you can confirm the signature check works before any customer mail depends on it. POST /v1/test/inbound goes further: with a test key, it pushes a fake inbound through the whole parse-and-classify path.
Endpoint counts are capped per plan: 5 on Free, 25 on Pro, 100 on Scale.
Add a webhook